Wednesday, April 13, 2011

Hackers and hacker ethics

Introduction
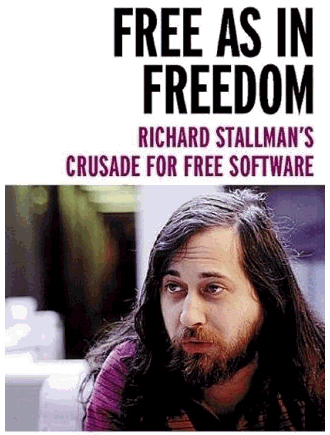
      In this essay, I explore the questions - what is a hacker? what do we mean by hacker ethic? with reference to Bryan Pfaffenberger's article "The social meaning of the personal computer : or, why the personal computer revolution was no revolution", Sherry Turkle's book "The second self" and the Discovery channel documentary "The history of hacking". Various aspects of hacking are discussed through the example of one of the greatest ethical hackers of 20th century, Richard Stallman.


What is a hacker?
       The Jargon file, a collection of hacker slang derived from technical cultures like MIT AI lab, defines a hacker as "A person who enjoys exploring the details of programmable systems and stretching their capabilities, as opposed to most users, who prefer to learn only the minimum necessary."
       Hackers that use their skills for good are called as "white hat" hackers. these white hats often work as certified "Ethical hackers", hired by companies to test the integrity of their system.
       We explore the culture of these white hat hackers and their hacker ethic through a view of life of Richard Stallman, one of the top 5 biggest white hat hackers ever existed.

Motivation behind hacking
       Captain Crunch, arguably the first "hacker" summarizes his motives beautifully in the following statement
"It's (the phone network) a beautiful system, you know. I want to work for her. I want to help her get rid of her flaws and become perfect."
       The idea of looking at the machine not as a means to end, but the end itself, originated by phone phreaks, more or less remains the central idea for computer hackers too.
        Stallman's crusade for software liberation started  with a printer. At the MIT lab, he and other hackers were allowed to modify the code of printer so that they sent convenient alert messages. However, a new printer came along - one that they were not allowed to modify. It was located away from the lab and the absence of alerts was a huge inconvenience. It was the point that he was "convinced... of the ethical need to require free software."
       
Hackers and the society
        As Sherry Turkle points out, hackers are closer to the computer than people. They are shy and inarticulate - trapped in the quest for control and mastery with the computers as their medium. Hackers tend to prefer relationships with computers than with humans. A major reason being computers can be "mold to their desires" - a world far less threatening and more rewarding than the world of conventional relations.
        Hackers find their true friend, soulmate in the computer. Computers provide refuce to their loneliness. Stallman is no exception. Text editor is program with which hackers spend most of their time. Stallman made a text editor which had a feature called "the doctor". The doctor was a program with which one could chat and the doctor would answer them intelligently. What a cure for loneliness!

Hacker ethics
         Hacker's obsession with computing leads to impatience and intolerance towards anything else that may come in the way. Following are some important beliefs in hacker ethics, as codified by Stephen  Levy.
  1. Access to computers should be unlimited and free.
  2. All information should be free.
  3. Mistrust the authority - promote decentralization.
        Stallman is an example of a hacker int whom, these beliefs are hardwired. He is considered, and rightly so, the father of free and open source software. He was against restricted computer access in lab. When a password system was installed, Stallman broke it down, resetting all the passwords to empty. He then sent messages to users informing them of removal of the system and promoting freedom with computer access.
        Stallman dedicated his life for freedom of software and information. He came up with the revolutionary concept of "copyleft". IT ensures that information required to modify/improve the program is always freely available.


Conclusion
         Although hackers tend to be isolated, they have made a great impact on the society - a positive one in case of white hat hackers. Naming of an asteriod after Stallman testifies his impact on the society.

Referecnes 
  1. The second self - Sherry Turkle
  2. The social meaning of the personal computer - Bryan Pfaffenberger
  3. Wikipedia
  4. Richard Stallman biography
  5. List of 10 greatest hackers : an article on www.itsecurity.com

Tuesday, April 12, 2011

Who is a Hacker?


Introduction
There is no one way to define a hacker. Hackers come in many varieties – Phone Phreakers, Network Hackers, Media Hackers, Hardware Hacker and so on. And while there is no one easy way to define a Hacker, one can observe, from their want for attention and their relentless disobedience of authority in their own pursuit of knowledge, that they are somewhat like a child – this analogy while not covering all the aspects of what it means to be a hacker, encompasses the essential aspects – Hackers ‘Do’ because they are curious, not for a cause, not for monetary gain and sometimes in this pursuit, they get caught as illustrated by Mitnick’s example. When Hackers do things, they bent the technology around them to achieve their goals, they never give into the constraints posed by the technology – infact one might go so far as to say that hackers really are just constraint benders and removers – and consequently are the Teasers at the Margin of technology. So while Hackers wield so much power in their hands (which arises from their juxtaposed tendencies to understand and control while also to be able to let loose and explore) , and when hacking culture gained momentum beginning with 1960s, a new set of ethical principles and a collective cultural view of society or at least how it should be arose in the eyes of the hacker leading to a established hacker subculture.

Ethics of the Hacker (?)

The Hacker ethic is essential to the idea of a Hacker Culture. It comprises of the set of rules and principles one must stick to in any situation, it is not a separate morality in itself but a product of the hacker’s world view. The product borne out of their mechanistic view of the universe and their thirst for understanding and conquering the “machine” - be it computer or telephone or in some cases even other people. 
Take for example Kevin Mitnick, one of the famous 20th century hackers, even though he was accessing proprietary information, he always claimed to do so for the joy of it - to know that he could do it, and when he kept this information, it was not for monetary gain but as a trophy to him, a proof of his abilities and the understanding he had in navigating the system. This highlights another important characteristic of the hacker, their need to feel that they can also influence control on the state of things - in Mitnick’s case, computer network technology, in other words, they feel a need for a decentralised scheme of things. Thus, Hacking is a means for them of ensuring that their world is not controlled solely by external factors. Another, major hacker is Richard Stallmanm, the founder of the free software movement, he became so engrossed with developing and making free the fruits of computer programming that he started the OpenSource movement which helped boost the hacker ideal of sharing and freeness of information. This too is another essential quality of hacker ethic - the idea of freeware and imbuing freedom of use to one’s creative products. 


In Conclusion
Often mistaken as hackers are the crackers who hack things not for the pleasure of understanding but maliciously with intent to injure and use the stolen information for illegitimate purposes, it must be noted that they are not operating in the true spirit of hacking as hacking seeks not to overthrow and control everyone but in it’s truest sense to try to embrace and understand technology and modify it for the better. The hacker is that mischievous and curious child near the sandbox in the playground not the Fist flinging bully near the swings.

Bibliography
1)     Wikipedia: Hacker Ethic, Hacker Culture, Richard Stallman, Kevin Mitnick
2)     Sherry Turkle, Hackers: Loving the Machine for Itself
3)     Pfaffenberger, The Social meaning of the Personal Computer
Barath

The Emerging Preprocessing Directive


Introduction
The subjection of routine tasks to mechanical means gained thrust in the industrial age where automation became the norm of the factory production. Although, automation initially was detested by workers for slashing their jobs (as can be seen in the agitations of the Luddites), these feelings reduced as the Industrial Revolution marched on due to the migration of skilled workers into other avenues of employment. Thus, automation even though faced with initial resistance, achieved its ultimate aim of making easy the processes of industry. With the advent of Computers post-WWII, it was only time before information and data were also automated. This too happened, with some resistance, but it has not been quite successful as it is yet to reach full potential, for while it automated data, it failed to informate it. I would like to discuss the essential difference between these two and the significance this understanding plays in contemporary life with help of an example.

The Difference and its Challenge              
Take the instance discussed in Alan November’s work Empowering Students with Technology of Schools where academic data records of students have been automated i.e. the schools have computerized the Grade Records of each Student and have made the calculation of functions based on these (say average, etc,.) automatic. This does automate the process of the making the Report Card of Students and hence is a definite improvement as it solves the problem with less effort than traditionally required but real informating this Data means to use it to give “more” information, achieve more control and make available more access than would be other not be possible – An explosion of new interactions and derivations with minimal effort enabled by the automating driving the informating. For example, with this computerization, the school could make the Grade card accessible to parents as an online Web-Grade Card which helps in tracking their Ward’s progress or they could schedule it to send emails to parents when their wards perform poorly or commend them when they do well. It could be used to inform the students themselves about the trend in previous years for electives chosen and how students before them performed, it could be used to help them find specific areas they need to concentrate on given their pursuit for higher education or it could even simply list the number of hours they need to put in to study based on their current score (possibly depending on a survey from previous batches of students). As can be easily realized, the variety of possibilities when one shuns the veil of automating and explores the possibility of informating are vast (even with such a small application as school student academic records) It only takes a little application, some insight and a little drive to achieve more than that offered by the plain platter of automation.


In Conclusion
As Technologists claim, we are in the Information Age and we need to take advantage of the possibilities offered by informating. The Main struggle against this currently I feel is the lack of understanding of the possibility offered by technology like the computer – most people do not know fully how to operate and take advantage of their computer, they are more than content with it for using it in sending, receiving email and surfing the web. This situation has to be remedied, at least by the next generation, where computer literacy should gain the foremost significance in education (both in spread and in depth) and an understanding of the essential difference people can make with computers (essentially a shift in people’s perspective from ‘computer as a tool for data crunching’ to ‘computer as a information deriver’), a complete integration of technology into education and work. With the realization of the vast possibilities of informating over plain automating, I feel confident that society will move towards this new information horizon and as we move through this stage of the information revolution - which is similar to what the initial stages of industrial revolution was for automating, I hope we will reach a time when informating, whose impact is currently only being realized in contemporary work life, will become an activity as mundane as automating - a preprocessing for newer and better analytics to come.

bibliography:
1) Alan November's Empowering Students with Technology
2)http://www.doug-johnson.com/dougwri/informate-not-automate.html


Barath A

What is the information panopticon? : Discussion with reference to the use of ICT in organization of work

Introduction
      The brainchild of 18th century English philosopher Jeremy Bentham, panopticon was an architectural innovation designed to lead to safe, humane prisons. The human tendency to think that, "every thing you do is right, until you get caught!" is what Bentham sought to curb using panopticon. The panopticon was engineered in such a way that, from a central tower, every prisoner in any cell could be observed., without the possibility of being observed by the prisoner.
       The central goal of panopticon was to achieve control through isolation and possibility of constant surveillance. The very thought of "somebody is watching us", in many cases, is  sufficient to keep the behavior under control, regardless of the fact that at the moment, nobody might be observing. Surprisingly, this idea was far more generic and was a good one for even schools, hospitals etc.


The information panopticon
        Realizing that in the modern, information centric world, control no longer requires physical domination over body, but can be achieved through isolation and constant possibility of observation, Michel Foucalt applied the idea of panopticon as a metaphor for the oppressive use of information in the modern disciplinary society.
        To gain control, all that is needed is complete knowledge and observation. In the information panopticon, we are seen without seeing the observers. The information is available without the knowledge of the subject. With the presence of such a panopticon, people need to regulate their own behavior to escape the constant threat of detection.
        The information panopticon is both literal and metaphorical. It manifests itself through public CCTV cameras, electronic monitoring of workers, face recognition and many more.

Information panopticon in use
        Soon after it was conceptualized, the idea was put into use. With ever increasing mechanization and automation, factory setting was a perfect place for a panopticon. Its modest roots can be traced back to the days when workers needed to swap their "punch cards" through a slot  in order to notify their arrival and departure. This simple setting, automatically did the job of keeping track of number of workers, their arrival and departure times automatically. This is good example of passive information collection.
        With the advent of internet, teh world has become a global village, and information sharehouse. But simultaneously, it became a source of distraction, unproductive wastage of time and money, if not used with control. The idea of information panopticon is central to organization of work in any modern corporation/organization/company whose employees work on computers. In this case, the panopticon is even more powerful by rendering itself invisible. With the use of advanced software, all the employees are being monitored in real time for their online activities. Websites which are found to distract the employees and waste a lot of productive time are being banned based on the collection by the panopticon.

Conclusion
        The notion of information panopticon has a great role to play in the moders information centric society. But this brings forth the question of integrity of those who are in power, the "observers" of the panopticon. The question "how much is too much?" must be addressed as the internet is being overpowered with services like google and facebook who are the bare essentials, information panopticons with vested, commercial interests.
       Limits are already being crossed. Facebook now decides whos is my best friend and who I must interact iwth. Google knows everything about me from how I plan my travel to what kind of information content is "relevant" to me.
       I conclude with an open question "who will observe the observers?"

Reference
  1. The virtual panopticon - David Engberg
  2. Surveillance 2.0 : The "information panopticon" and education - Larry Kuhen

Friday, April 8, 2011

The Information Panopticon


It was very early on that Man realised that any organized work or activity requires some sort of supervision. It is for the sake of supervision that there are hierarchies in every organization. Supervision was even built into the architecture of buildings like schools, banks, prisons and hospitals; the supervising authority had an overview or a “panopticon” of the subjects, by which they could examine the activity and status of each and every one of the subjects. This is carried on to the present in the form of the Information Panopticon, where we are constantly being supervised with the help of technology.

Michel Foucault, in his book Discipline and Punish: The Birth of the Prison gave examples of this kind of architecture. A prison, for example, had a central tower in which a guard was housed. The tower was surrounded by the cells. Hence, the guards could easily supervise the inmates. Even in many schools, the classrooms are arranged in a circle for easy supervision. Inside the classrooms, the teacher stands on a raised platform and can monitor students. In hospitals, all the wards would be transparent so that the status of the patient could be checked on any time.


Today, supervision by architecture has been replaced by supervision by computers. As much of our work today involves some kind of computer operation like running a program, creating a document or sending an email, this supervision becomes easy. The time stamp on our work automatically tells the boss when the job was done. A striking observation of this is that the supervising entity cannot be negotiated with or pleaded with. As always, the replacement of man by machine brings in some kind of rigidity. The machine simply does what it is programmed to do; neither does it need to negotiate with the subordinates nor does it need to listen to their excuses. Thus, the information panopticon has this impact on our work lives. Let us take for example the computerisation of British banking industry in the 70’s and early 80’s.

In British banking the traditional mode of training prior to computerization was based on a master-apprentice model, according to Steve Smith (1989). Employment began at age 15 or 16, and one then rose level by level through a pyramidal hierarchy. Ultimately, with luck and aptitude, any employee could hope to become manager of a branch bank or even a general manager at corporate headquarters. Along with this career structure went an ethos of employee flexibility. Clerks had a relatively wide range of skills, allowing them to shift from task to task during the banking day. British bankers installed computers as part of a general plan to move away from the craft-apprenticeship model toward a rationalized industrial production model. Computers facilitated, for example, progressive specialization of tasks and automation of a great deal of work once done by hand. Along with this specialization went a deliberate restructuring of career paths.

Thus, we can see that the use information panopticon in our work lives can bring about radical changes not only to the structure of the work system but also to the skill set and the attitude of the individual workers. But we can safely say that this change is for the better since it leads to greater efficiency and productivity.


By Pranav R Kamat

References:
Michel Foucault, “Discipline and Punish: The Birth of the Prison”

Monday, March 28, 2011

The Cold War – Risks and Responsibilities


In the article by Paul Edwards, it is stressed that the US defence was the single most important reason for the development of advanced computers. The arms race and the technological competition between the US and the Soviet Union in the Cold War period resulted in extensive scientific research, which gave birth to computers. But there is a certain risk involved in this justification.


Risk, in this context, has a more subtle meaning. Take for example, the EVMs (Electronic Voting Machines) in India. It was discovered by a software engineer that that these EVMs could be hacked into and the poll results could be viewed and changed. In fact, the hacking was possible in two ways – one, by using a Bluetooth connection and a hacking code and two, by tampering with an easily detachable memory chip that recorded the votes of hundreds of voters.  The Election Commission, by neglecting this huge flaw, has put millions of Indian citizens at risk. The single most important aspect of the Indian governance – democracy – could be potentially mean nothing if the poll results did not reflect the choice of voters. Therefore it is crucial for the Election Commission to take responsibility for its slackness. After all, the Election Commission is the only link, although weak, between Indians citizens and their government.


Coming back to the Cold War context, the risk factor by such a justification is the assumption that computers would not have been developed if not for the perceived need for national security by the US. It is a heavy thought for all of us that our PCs are a result of military research and that they were developed from the ENIAC - the machine that computed ballistics tables for missiles that killed thousands of people.

By Pranav R Kamat

References:
1. The Risks Digest
2. From “Impact” to Social Process: Computers in Society and Culture by Paul Edwards
3. An Unforseen Revolution: Computers and Expectations, 1935 - 1985 by Paul Ceruzzi

Sunday, March 27, 2011

Risks and Responsibilties: Cold War and Now


Introduction
Though Computers were used for limited activities during the Second World War, their potential to decisively change the course of wars was realized as evidenced in the cracking of Nazi Ciphers by Britain’s Colossus Computer. This led to a sustained funding for scientific research of military interest during the Cold War. This Research was mainly conducted by Civilian and Industrial Laboratories in association with the military. The Main reason for this technophilic trend essentially boils down to the conflicts which existed on the economic, political front between Communist Nations and the Western countries. This led to fears of another War like WWII and led to the amassing of weapons of Mass Destruction and the drive to further the development of the computer. This kind of a justification for scientific research based on possibility of a war i.e. a threat to national security, though fruitful had its own risks and a set of associated responsibilities which were needed in order to avert accidental disasters or oversights. I would like to discuss this aspect with a relevant example from the present time.

A Modern Day Example
The Electronic Voting System was started as a means to counter possible corruption and manipulation of Votes through the Ballot system in India. For the success of a Democratic nation, a safe and secure method of conducting voting is essential and technological research aimed at solving these problems in light of its importance to national security, has some possible risks and inherent responsibilities associated with it. For instance, the System has to be foolproof and be backed up so as to prevent any power outage from affecting it – which was realized and done so. Also, it should be ideally tamperproof, but as can be seen with the current EVMs in India, they are far from tamper proof. These Machines can be manipulated in various ways as shown by Hari Prasad and Group. While normal ballot system involved criminals cheating by manipulating the votes afterward during storage phase, no safe guard was developed in the Electronic system against a similar attack by more tech savvy criminals. Then how come EVMs have been claimed to be better than the normal system?

 The Justification from officials is that it is “safer” than the human controlled system which can be tampered easily but this view has remained legitimate and largely unquestioned due to the fact that common folk (which includes these officials who are not trained professionally in these technologies) while very well understanding the concept of human error, are not familiar with the concept of computer error, and this has been the key then and now for the perceived safety in these systems. For example, the SAGE defense system which was made in America had one goal in mind – to show the citizens of the US that they were ready to react to the threat of Nuclear Weapons. However, in hindsight it has been shown that the SAGE system while inspiring and advancing Technology was not capable of handling the threat - it was little more than a stunt. In fact, in the past, a major Nuclear Incident was averted because of the correct handling by the human operator in charge of overseeing the system who on seeing that SAGE showed the US being attacked by a multitude of Missiles realized that it was actually a glitch in the system that had caused this and did not report it to his higher officers thus saving the world from M.A.D. 

In Conclusion
While safeguards were taken in both cases, these were not enough in the sense that they did not anticipate certain key ways the system would fail. The sense of threat to national security which was perceived to be greater before the usage of Electronic systems, led to these machines not being tested adequately before going live. Thus, a key responsibility that the developers of these systems have is to test the reliability of these systems as this is the very reason they are replacing the current system. The system developed have to be made accountable to professionally capable people who can access the real value of these systems and not be distorted in their judgment due to a one sided knowledge based on a unreal idea of the safety in using Electronic systems against a perceived threat to security of the nation.

Bibliography

1)      1)From Impact to Social Process :Computer in Society and Culture , Paul Edwards
2)      2)The Risks Digest, http://catless.ncl.ac.uk/risks
3)      3)http://indiaevm.org/
Barath A